Hackers Exploit Microsoft’s X Account to Push Dubious “Clippy” Crypto Token
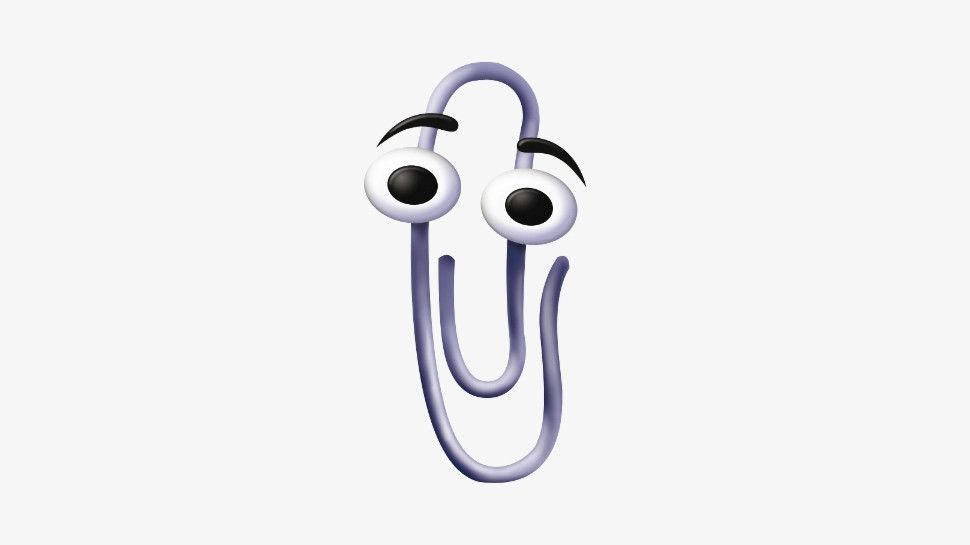
Microsoft confirmed that its official X (formerly Twitter) account was compromised on Tuesday, with attackers using the platform to market a newly minted cryptocurrency token named $CLIPPY, a reference to the company’s long‑disliked paper‑clip assistant.
The intruders posted a series of promotional messages that mimicked the style of Microsoft communications, including a fabricated apology that claimed the company was “launching an innovative digital asset.” The posts also featured a logo that closely resembled Microsoft’s branding, a tactic designed to lend credibility to the scam.
Within minutes, the fraudulent tweets were amplified through retweets and replies from accounts that appeared to be affiliated with Microsoft, further spreading the lure of a quick‑profit opportunity tied to the nostalgic Clippy mascot. The scheme promised high returns for early investors, a common lure in the wave of crypto‑related fraud that has plagued social media platforms in recent months.
Microsoft’s security team responded promptly, confirming that the account had been accessed without authorization. The company removed the offending content, reset credentials, and implemented additional safeguards to prevent future breaches. In a brief statement, Microsoft emphasized that it does not endorse any cryptocurrency and warned users to be skeptical of unsolicited investment pitches.
Cybersecurity experts note that hijacking verified corporate accounts is an effective way for fraudsters to bypass typical trust barriers. By leveraging a well‑known brand and a nostalgic cultural icon, the attackers increased the likelihood that users would click on malicious links or purchase the token. The incident underscores ongoing challenges as regulators and platforms grapple with the rapid growth of decentralized finance and the ease with which digital identities can be spoofed.
Authorities have not yet identified the individuals behind the breach, but law‑enforcement agencies are monitoring the situation for potential financial crimes. Meanwhile, security advisors recommend that users verify the authenticity of any crypto‑related announcements directly with the issuing company, enable multi‑factor authentication on social media accounts, and remain cautious of offers that sound too good to be true.
Comments (0)
Be the first to comment.
Join the discussion