ASOS Confirms Investigation After Fake App Alert Claims Data Breach
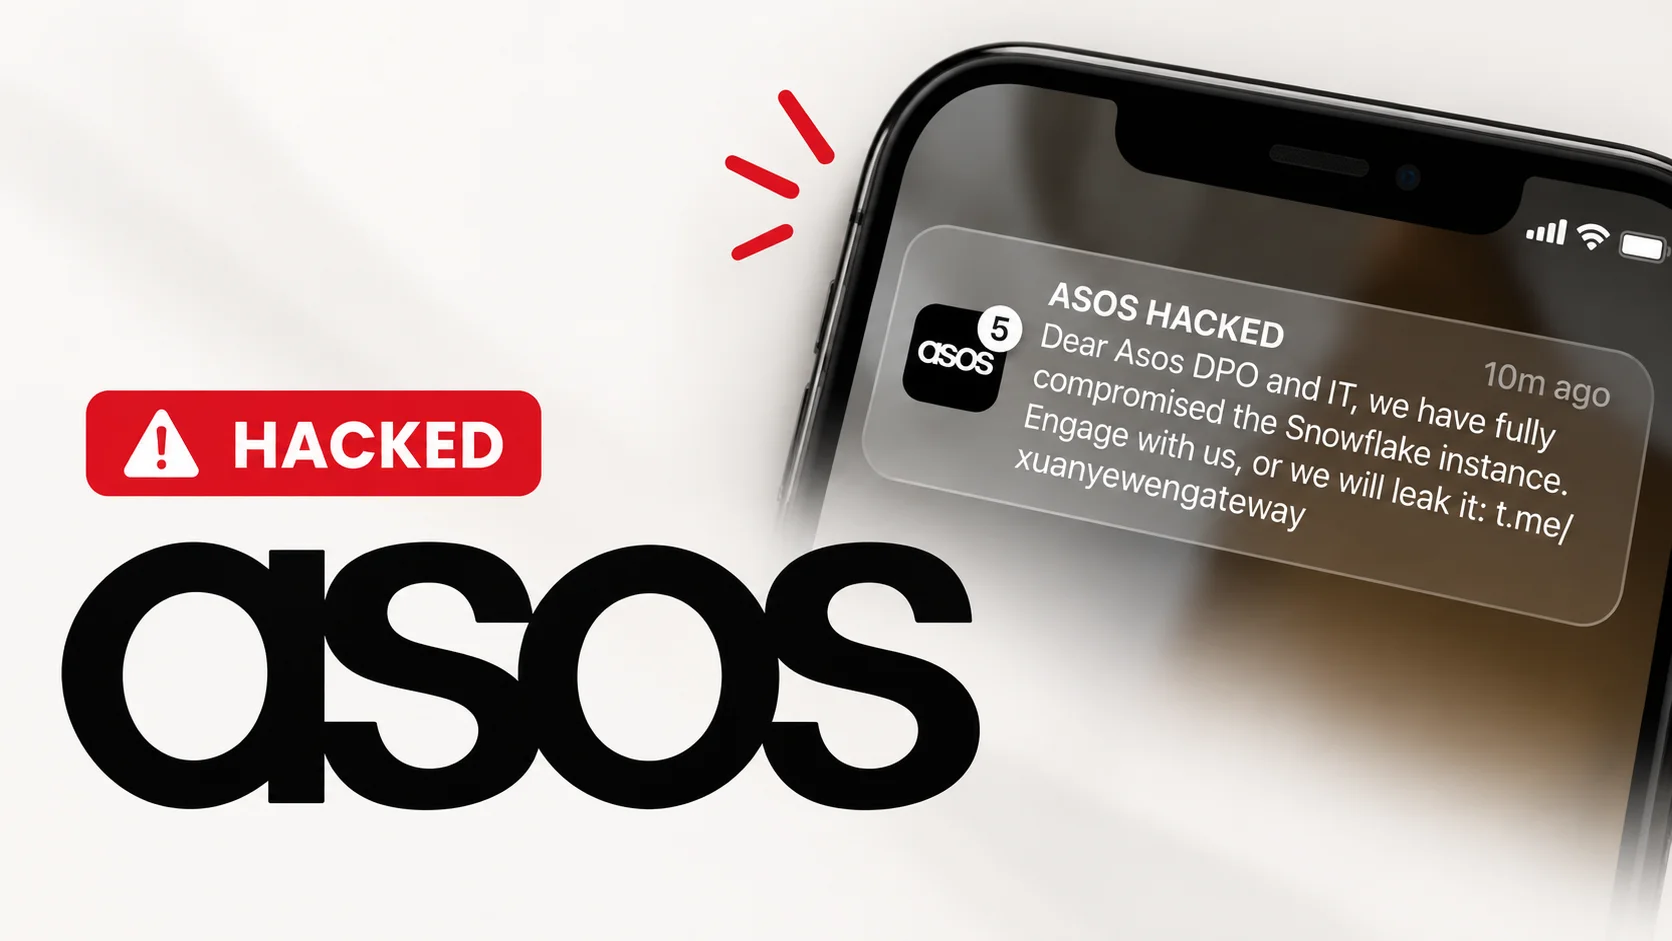
Online fashion retailer ASOS said it is probing a cyber incident after shoppers reported receiving an unexpected push notification through the company’s mobile app that alleged hackers had infiltrated its Snowflake data environment.
The alert, which appeared to come from ASOS, warned users that personal information might have been compromised and urged them to take precautionary steps. Recipients described the message as “official‑looking,” and several posted screenshots on social media before the retailer issued a statement.
In a brief response, ASOS confirmed that it had detected “suspicious activity involving third‑party communication platforms” and was working with internal and external experts to determine the source of the unauthorized notification. The company stopped short of confirming any actual breach of its Snowflake data warehouse, noting that investigations were ongoing and that no evidence of data exfiltration had been found at the time of the announcement.
Snowflake is a cloud‑based data‑warehousing service widely used by retailers to store and analyze customer and transaction information. Because it aggregates large volumes of personally identifiable data, any unauthorized access would raise significant privacy concerns and could trigger regulatory reporting obligations under laws such as the UK GDPR. Cyber‑actors often exploit the perception of legitimacy that a Snowflake breach conveys to sow panic and extract further information.
The episode arrives amid a wave of cyber threats targeting the retail sector, where attackers frequently leverage compromised third‑party services—such as messaging or notification providers—to distribute fraudulent communications. Recent high‑profile incidents at other fashion and e‑commerce firms have highlighted the challenge of securing supply‑chain connections that sit outside an organization’s direct control.
ASOS said it has engaged forensic specialists to trace the origin of the push notification and assess whether any data was accessed or copied. The retailer also indicated it would cooperate with relevant data‑protection authorities and, if necessary, inform affected customers in accordance with regulatory requirements. Security experts suggest that the outcome of the investigation will shape how the company and its peers reinforce safeguards around third‑party integrations and user‑facing communication channels.

Comments (0)
Be the first to comment.
Join the discussion